

Overview
What is NIST SP 800-171?
NIST SP 800-171 specifies security requirements for protecting Controlled Unclassified Information (CUI) in nonfederal systems and organizations. Whether it applies to your organization, and which revision is required, depends on the relevant contract or other governing requirement. Revision 3 was published in May 2024; some contractual requirements may continue to reference Revision 2.
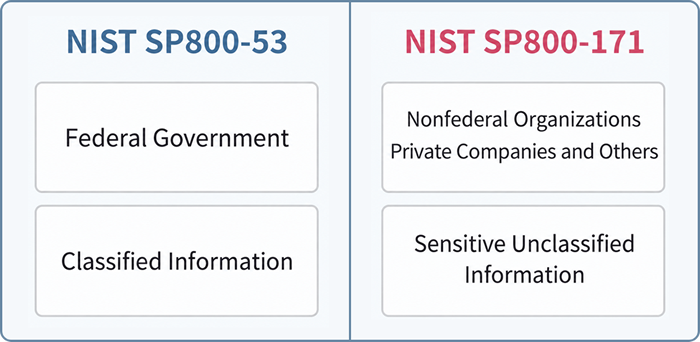
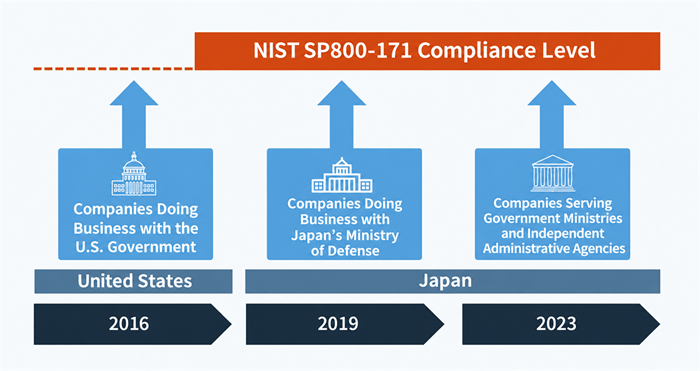
We help organizations identify the requirements relevant to the information they handle and the customers they serve.
Purpose and Value of Our Service
We assess your current controls against the applicable requirements, identify gaps, and develop a prioritized remediation plan. Our support can include policies and procedures, implementation assistance, evidence preparation, and mock audits. The resulting reports explain the status of implementation and the actions still required.
Why Choose Us
- Extensive NIST Compliance Experience
- We have supported numerous defense-related companies, manufacturers, IT companies, and other organizations in their efforts to comply with NIST SP 800-171. Our accumulated expertise gives us a deep understanding of industry-specific challenges and enables us to achieve compliance through effective, tailored approaches.
- Consultants with Advanced Professional Credentials
- Our consultants hold internationally recognized security credentials, including CISSP, CISA, and CISSO, and have experience interpreting requirements and supporting implementation.
- Hands-On Support Through Implementation
- We go beyond simply providing a checklist and deliver support designed for real-world operations. From developing security policies and procedures to recommending specific technical configuration changes and training your personnel, we work alongside your team to build a security program that functions effectively in practice.
Our Service Process
-
- 1 Kickoff and Current-State Interviews
- We begin the project with a kickoff meeting. Through interviews with senior management and relevant departments, we identify the scope of the CUI you handle, assess your existing security measures, and finalize the project structure and schedule.
-
- 2 Current-State Assessment and Gap Analysis
- We evaluate your existing administrative and technical controls against every NIST SP 800-171 requirement. By reviewing policies and system configurations and interviewing responsible personnel, we identify controls that have not been implemented or are insufficient. Based on the findings, we prepare a gap analysis report that clearly defines the required improvements.
-
- 3 Remediation Planning and Implementation Support
- Based on the gap analysis, we develop a remediation roadmap for achieving compliance. This defines specific measures for each requirement, such as strengthening access controls, introducing cryptographic modules, reviewing multi-factor authentication processes, and improving physical security. We support implementation activities—including policy revisions and system configuration changes—in line with the plan, and provide project management and technical assistance as needed.
-
- 4 Mock Audit (Internal Audit)
- After the measures have been implemented, we conduct a mock audit using procedures comparable to those of an actual audit. Following a NIST SP 800-171 checklist, we review documentation, verify systems, interview relevant personnel, and assess implementation status. We also collect supporting logs and records and verify conformity with every requirement. This internal audit identifies any remaining issues, and we provide findings and recommendations wherever corrective action is needed.
-
- 5 Audit Report and Improvement Recommendations
- We prepare and present an audit findings report summarizing the results of the mock audit. The report documents the conformity or nonconformity determination and supporting evidence for each requirement, along with specific improvement recommendations for any nonconformities. At a reporting meeting, we explain the results to management and responsible personnel and advise on any additional actions required. Our ultimate goal is to bring your organization to a point where it can confidently demonstrate compliance with NIST SP 800-171.
Key Deliverables (Examples)
- Current-State Assessment and Gap Analysis Report
- A report detailing the differences between your current security program and the NIST SP 800-171 requirements. High-risk gaps and remediation priorities are presented at a glance.
- NIST SP 800-171 Compliance Plan
- A plan listing the measures required to achieve compliance. It identifies action items, responsible parties, and schedules, serving as a practical implementation roadmap.
- Security Policies and Procedures
- We prepare new and revised policies, standards, and operating procedures needed to meet NIST SP 800-171. These may include an information security policy, access-control procedures, and incident-response procedures.
- Audit Checklist and Evidence Register
- An audit checklist covering every NIST SP 800-171 requirement, together with a register of implementation evidence for each requirement. These materials can be used during both internal and formal audits.
- Audit Findings Report
- A report summarizing mock audit findings, supporting evidence, and recommended improvements. It supports management decisions and preparation for customer or other required assessments.
Organizations We Support
- Defense Industry Organizations
- Companies involved in Ministry of Defense procurement or handling defense equipment and military technology, as well as organizations in domestic and international defense supply chains that must meet advanced security standards.
- Companies Doing Business with U.S. Organizations
- Companies that provide products or services to U.S. government agencies or the U.S. military, or that are required by U.S. customers or business partners to comply with NIST SP 800-171. This includes organizations across a wide range of industries, including aerospace, manufacturing, and technology.
- Companies with Global Operations
- Companies operating in international markets that want to establish a security program aligned with global standards, as well as organizations strengthening security to enhance trust in international transactions or prepare for future CMMC certification.
Estimated Timeline and Fees
The duration of our service varies depending on the scope of support and the number of systems involved. The shortest projects typically take approximately four months from kickoff to final reporting, while a standard project generally takes around six months. We can flexibly adjust the schedule to suit your organization's needs.
Fees are quoted individually based on the size of your organization and the scope of support required. Contact us to discuss your requirements, and we will recommend an appropriate plan and provide an estimate. We offer flexible options tailored to your budget and needs, so please feel free to get in touch.
Contact us to discuss the requirements in your contracts, the systems in scope, and your target schedule.
