

Transform post-certification ISO operations from a person-dependent task into a reliable monthly process.
Effective Post-Certification Operations Make the Difference
Maintaining ISO certification requires more than simply having policies in place. Certification bodies verify that activities such as risk assessments, control operation, training, internal audits, management reviews, and corrective actions are performed continuously and supported by clear records.
-
- Common Operational Challenges
-
- Work is concentrated on the person in charge immediately before an audit.
- Risk assessments and control reviews are performed only once a year.
- Evidence such as training records, supplier evaluations, and access-right reviews is scattered across multiple locations.
- Internal audits become checklist exercises and fail to drive improvement.
- Management review inputs and outputs are incomplete.
- Changes to standards, laws, and guidelines are difficult to keep up with.
-
- How Outsourcing Addresses These Challenges
-
- Collect and organize records monthly based on an annual plan.
- Integrate the requirements of multiple standards to reduce duplicate work.
- Organize evidence into audit-ready packages that are easy to explain.
- Design internal audits and corrective actions as improvement activities.
- Visualize the information senior management needs to make decisions.
- Incorporate checks for new editions and transition requirements into routine operations.
How This Service Works
-
- Full-Service Outsourcing
- Our external team leads secretariat tasks, record maintenance, internal audit preparation, and certification audit support.
-
- Collaborative Operations
- You retain responsibility for approvals, decision-making, and providing operational information while minimizing your administrative workload.
-
- Continual Improvement
- We go beyond one-time responses to nonconformities and observations, tracking corrective actions through to recurrence prevention.
What is ISO Management System Outsourcing?
This service provides a specialist team to perform and manage the monthly operational tasks required to maintain ISO/IEC 27001, 27017, 27701, and 42001 certifications. We provide more than advice: we continuously maintain the records, reviews, and improvements examined during audits.
ISO Management System Outsourcing at a Glance
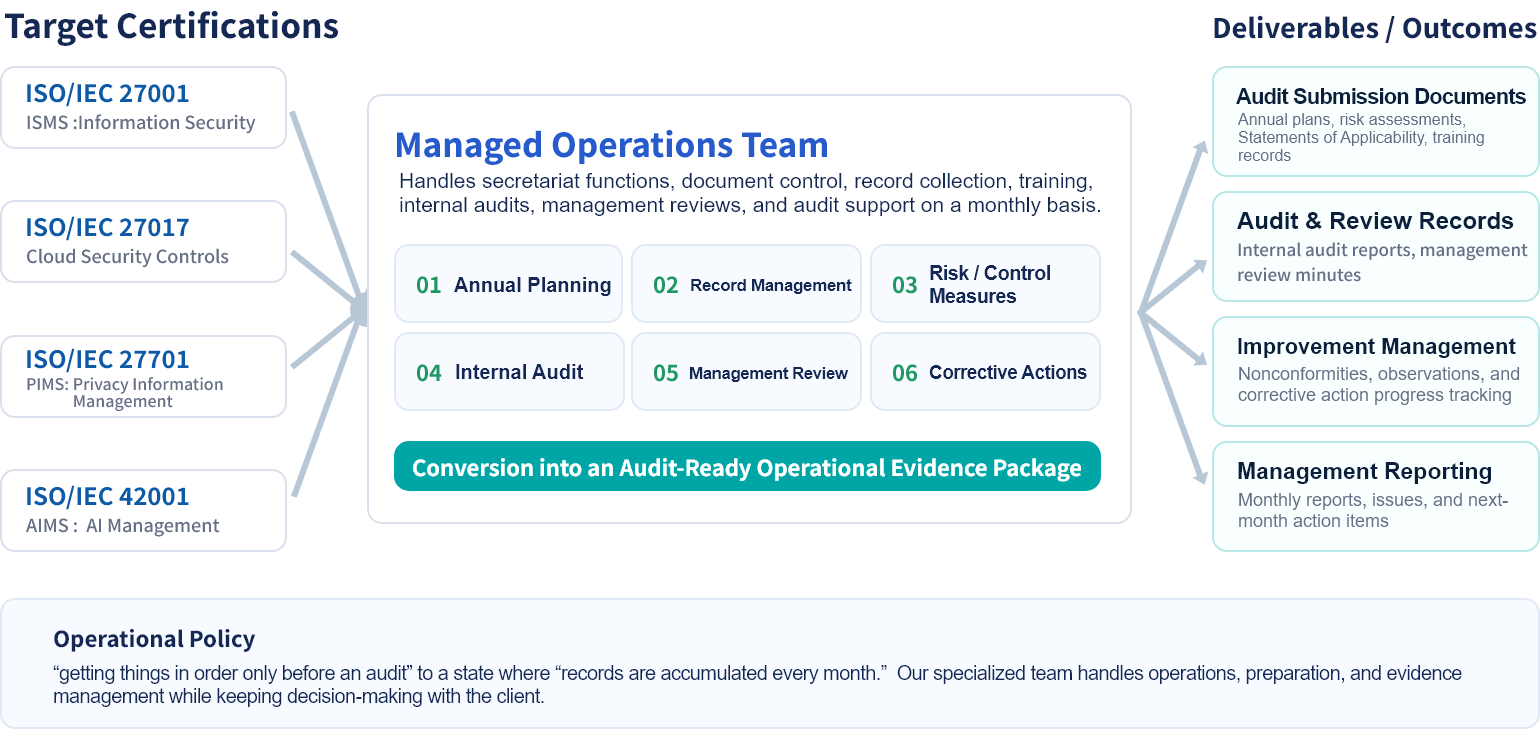
-
- Operate Monthly
- Build operational logs and evidence each month instead of preparing only immediately before an audit.
-
- Integrate Multiple Standards
- Use ISO/IEC 27001 as the foundation and organize cloud, privacy, and AI requirements without duplication.
-
- Be Ready to Explain Your Operations
- Prepare policies, forms, meeting minutes, and audit reports at the level of detail needed for an audit.
Applicable Standards and Our Approach to Integrated Operations
Managing information security, cloud security, privacy, and AI governance separately leads to duplicate records and meetings. This service uses ISO/IEC 27001 as its foundation and maps the requirements specific to each standard into an integrated management matrix.
| Standard | Operational Area | Key Audit Focus Areas | Operational Considerations |
|---|---|---|---|
| ISO/IEC 27001:2022 | ISMS | Information Security Management System. Key areas include risk assessments, controls, the Statement of Applicability, internal audits, and management reviews. | ISO/IEC 27001:2022/Amd 1:2024 (climate change amendment) must also be reviewed. |
| ISO/IEC 27017 | Cloud Security | Extends ISO/IEC 27002-based controls for cloud service providers and customers. Reviews shared responsibilities, configuration management, logging, virtualization, data deletion, and related areas. | As of July 2026, the second edition is in the publication stage. Confirm the transition policy from the 2015 edition with the certification body. |
| ISO/IEC 27701:2025 | PIMS | Privacy Information Management System. Establishes responsibilities for PII controllers and processors, personal information processing, consent, suppliers, and data subject rights. | The 2019 edition has been withdrawn. Confirm transition deadlines and audit conditions for existing certifications. |
| ISO/IEC 42001:2023 | AIMS | AI Management System. Establishes processes for AI use and provision risks, impact assessments, monitoring, transparency, accountability, and lifecycle management. | Maintaining evidence of AI inventories, AI risk assessments, AI policies, and accountability structures is essential. |
Reduce Duplication Through Integrated Operations
-
- Document Management
- Standardize policies, scope, organizational structure, roles, and responsibilities, and manage only standard-specific requirements separately.
-
- Risk Assessment
- Link and assess information assets, cloud services, personal information, and AI systems in a single register.
-
- Audits and Reviews
- Combine internal audits and management reviews while adding checkpoints specific to each standard.
Scope of Services
We perform the practical work required to maintain certification across three levels: annual planning, monthly operations, and annual audit support. This allows you to focus on decisions, providing operational information, and management judgment.
-
- ISO Secretariat Services
- We manage annual plans, meeting schedules, issue tracking, audit schedules, and the progress of evidence collection.
-
- Risk and Control Management
- We update risk assessments, risk treatment plans, the Statement of Applicability, and control effectiveness reviews.
-
- Objective and KPI Management
- We establish security, privacy, and AI governance objectives and review actual performance against plans and improvement progress each month.
-
- Document and Record Management
- We organize assessments, access-right reviews, and related records for audits.
-
- Internal Audits
- We create audit plans, checklists, and reports based on standard requirements and actual business operations, using the results to drive improvement.
-
- Management Reviews
- We collect the required inputs and document management decisions, instructions, and outputs in meeting minutes.
-
- Education and Training
- We support training for secretariat staff, managers, and employees, along with comprehension checks, attendance records, and follow-up for those who have not completed training.
-
- External Audit Support
- We support audit preparation, anticipated questions and answers, attendance on the audit day, organization of findings, and preparation of corrective action plans.
-
- Legal and Guideline Reviews
- We review applicable laws, contractual requirements, industry guidelines, and updates to standards and revise documentation as needed.
Exclusions and Important Notes
- Certification bodies make the final decision on granting and maintaining certification; therefore, we do not guarantee a successful audit result.
- You remain responsible for management decisions, risk acceptance, legal decisions, and formal responses to certification bodies.
- Audit fees, certification registration fees, travel expenses, third-party system fees, and advice from legal professionals are charged separately.
Annual Operating Model
Effective ISO operations require a design that builds evidence monthly, reviews effectiveness quarterly, and connects these activities to annual internal audits, management reviews, and external audits.
Sample Annual Operations Calendar
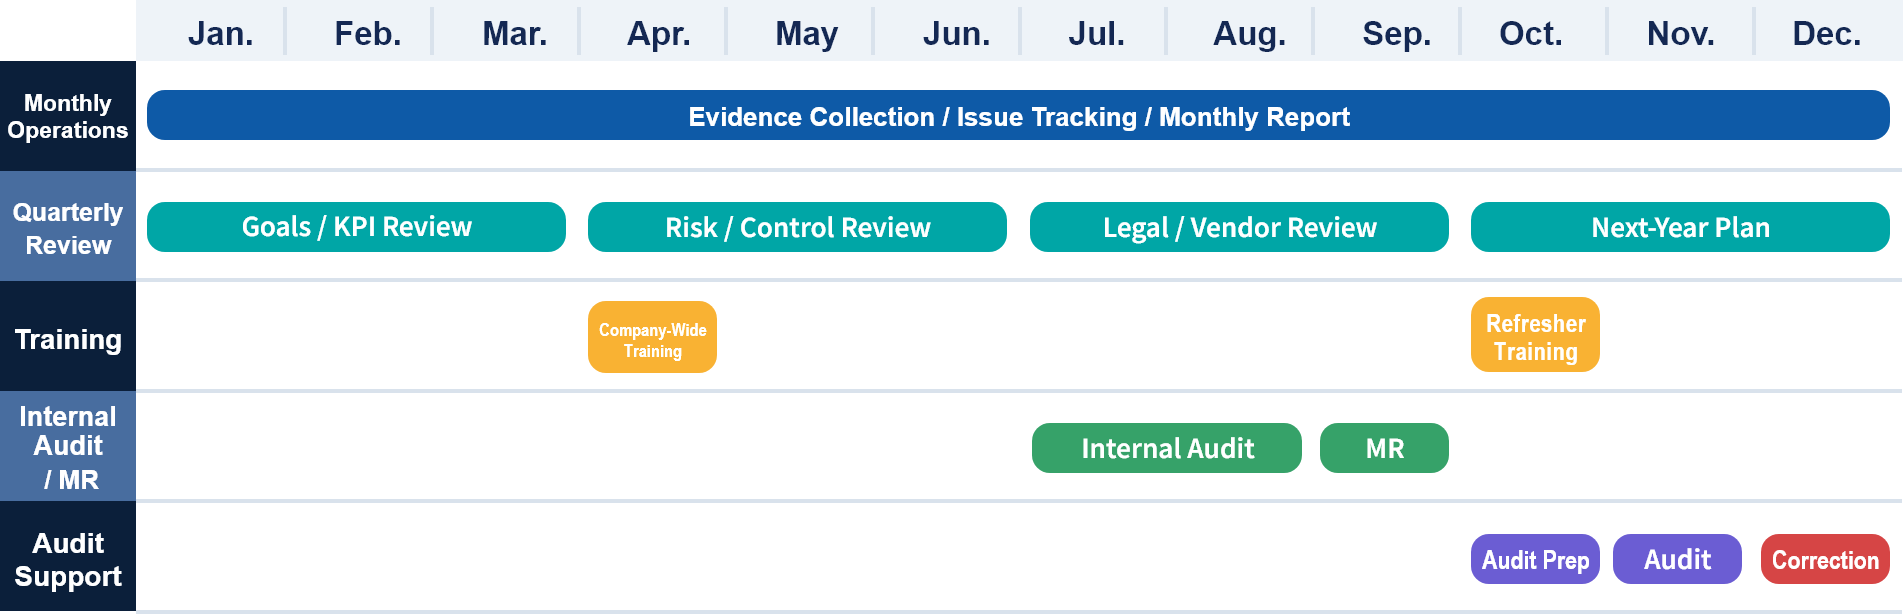
Key point: Maintain monthly operational logs in a form that can be used directly as audit evidence, instead of rushing to prepare documents immediately before an audit.
PDCA Operating Model for Maintaining Certification
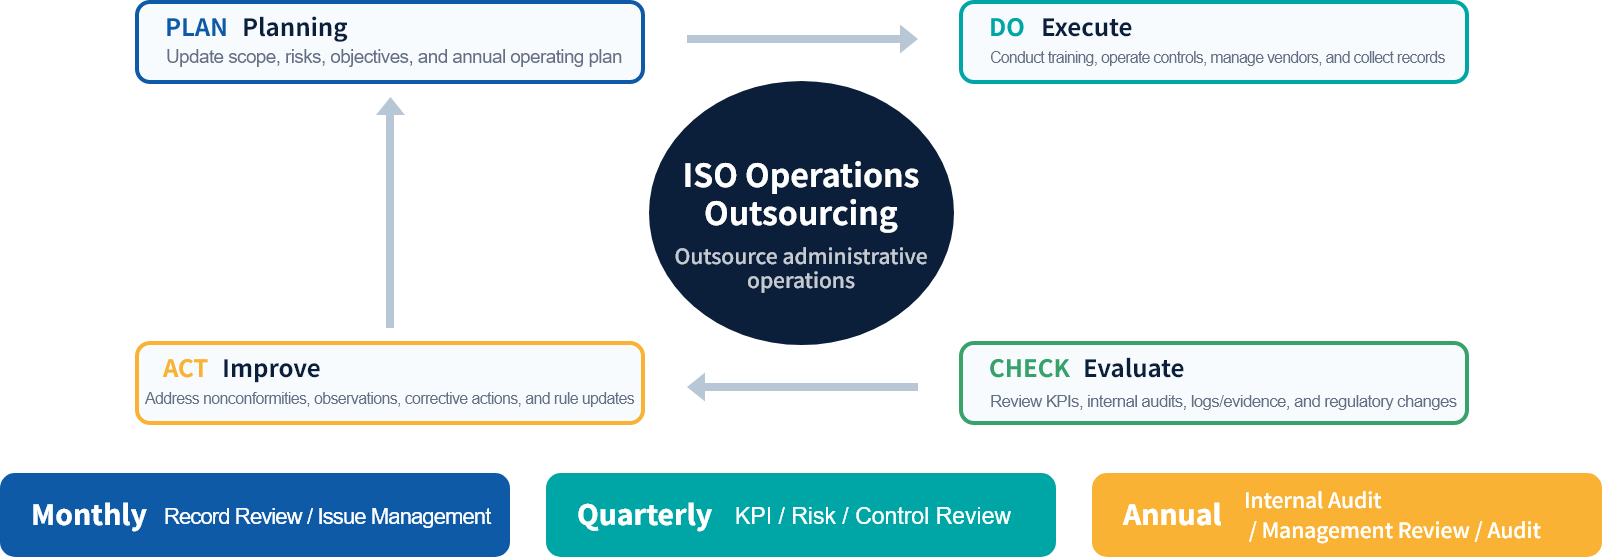
Key point: Maintain monthly operational logs in a form that can be used directly as audit evidence, instead of rushing to prepare documents immediately before an audit.
Implementation Process
Starting with your current certification status and findings from the previous audit, we define the necessary operating model and deliverables. We make use of your existing documents to create a practical process without adding excessive rules.
From Implementation to Stable Operations
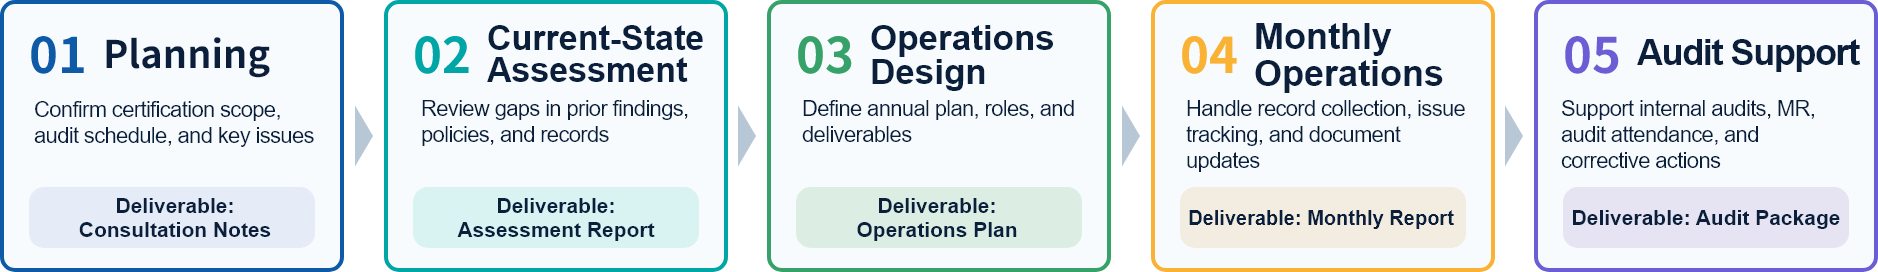
We conduct an initial assessment based on your previous audit report, certification documents, policies, and forms so that monthly operations can begin as early as the following month.
-
- Documents You Will Need to Provide
- Certification documents, the previous audit report, policies and forms, an organization chart, the scope of certification, risk assessment tables, and related materials.
-
- Initial Assessment Focus Areas
- Current document versions, incomplete corrective actions, the status of internal audits and management reviews, and evidence relating to training, suppliers, and access rights.
-
- Regular Operations After Launch
- Monthly meetings, issue registers, evidence collection, actions for the following month, and a schedule planned backward from the audit date.
Pricing Plans
Pricing varies according to the number of applicable standards, locations, and employees, the audit schedule, and the condition of existing documentation. The following prices are provided as a reference. A formal quote will be provided after the initial assessment.
| Plan | Purpose | Reference Price (Excluding Tax) | Main Services | Recommended For |
|---|---|---|---|---|
| Starter | Stabilizing Operations for a Single Standard | From JPY 120,000 per Month | Monthly meetings, annual planning, record reviews, and audit preparation advice | Organizations that already have generally effective operations for a single standard, such as ISO/IEC 27001 |
| Standard | Secretariat Services for Multiple Standards | From JPY 150,000 per Month | Monthly operations, document and record maintenance, objective management, internal audit and management review support, and audit preparation | Organizations maintaining ISO/IEC 27001 together with ISO/IEC 27017, 27701, or 42001 |
| Full Outsourcing | Full Outsourcing of Certification Maintenance | From JPY 250,000 per Month | Secretariat services, evidence collection, internal audits, management reviews, audit attendance, corrective actions, and reviews of standard revisions | Organizations seeking integrated operation of ISO/IEC 27001, 27017, 27701, and 42001 |
| Spot | Focused Support for Recertification and Surveillance Audits | From JPY 150,000 per Engagement | Short-term gap assessment, audit document preparation, anticipated questions and answers, and corrective action plans for findings | Organizations with missing documentation shortly before an audit or unresolved findings from the previous audit |
Items Not Included in the Fees
-
- Main Costs Quoted Separately
-
- Certification body audit and registration fees
- Travel and accommodation expenses when on-site visits are required
- Third-party system fees for e-learning platforms, GRC tools, and similar services
- Large-scale policy restructuring and new certification projects
-
- Factors That Affect Pricing
-
- Number of applicable standards, locations, departments, and employees
- Scope of cloud, personal information, and AI use
- Number and status of unresolved findings from the previous audit
- Scope of internal audits performed by us
Key Deliverables and Responsibilities
The most effective outsourcing model is one in which the external team leads the work while you provide operational information and final approval.
| Deliverable | Description | Responsibilities |
|---|---|---|
| Annual Operations Plan | Monthly, quarterly, and annual task plans scheduled backward from the audit month | Prepared by us / Approved by you |
| Integrated Requirements and Controls Register | Maps ISO/IEC 27001, 27017, 27701, and 42001 requirements to supporting evidence | Prepared by us / Reviewed jointly |
| Risk Assessment and Treatment Plan | Risk assessment covering information assets, cloud services, personal information, and AI use | Updated by us / Decisions made by you |
| Objectives and KPI Tracking Table | Monthly tracking of objectives, results, reasons for shortfalls, and improvement measures | Compiled by us / Confirmed by you |
| Training Records and Comprehension Checks | Target participants, completion status, follow-up for incomplete training, and comprehension tests | Managed by us / Communicated internally by you |
| Internal Audit Report | Audit plan, checklist, findings, and improvement recommendations | Conducted and prepared by us / Reviewed jointly |
| Management Review Minutes | Inputs, management decisions, instructions, and outputs | Drafted by us / Decisions made by senior management |
| Audit Support Package | Submission documents, anticipated questions and answers, findings management, and corrective action plans | Prepared by us / Handled jointly |
Principles for Assigning Responsibilities
-
- Led by Us
- Operations planning, task management, proposed document and form updates, evidence organization, preparation of audit materials, and improvement management.
-
- Handled by You
- Management decisions, risk acceptance, final approvals, provision of operational information, internal communication, and policy implementation.
-
- Handled Jointly
- Internal audits, management reviews, external audits, responses to findings, and corrective actions.
Frequently Asked Questions (FAQ)
- Can we continue using our existing policies and forms?
- As a rule, we make use of your existing documents. We propose revisions only where content is difficult to explain during an audit, does not align with revisions to standards, or differs from actual operations.
- Can standards other than ISO/IEC 27001 be managed together?
- Yes. Using ISO/IEC 27001 as the foundation, we organize the specific requirements of ISO/IEC 27017, 27701, and 42001 in an integrated management matrix and combine their audits and reviews.
- Can you attend the audit?
- Yes. We can attend remotely or on-site to support document presentation, response planning, review of findings, and development of corrective action policies.
- Can we engage your services immediately before an audit?
- Yes. However, if significant records are missing, we begin with short-term support that includes a gap assessment, prioritized organization of required evidence, and preparation of a corrective action plan.
Standards Information Notes (as of July 2026)
This document reflects the official names, edition numbers, and transition status of the standards and includes confirmation of certification body transition policies as an operational task. Please check the latest guidance from accreditation and certification bodies for official requirements, transition deadlines, and audit applicability dates.
| Standard | Description in This Document | Source |
|---|---|---|
| ISO/IEC 27001:2022 | Requirements for an Information Security Management System (ISMS). Amd 1:2024 is also included in the review. | Official ISO page: ISO/IEC 27001:2022 |
| ISO/IEC 27017 | Information security controls for cloud services. As of July 2026, the second edition is in the publication stage. | Official ISO page: ISO/IEC 27017 |
| ISO/IEC 27701:2025 | Requirements and guidance for a Privacy Information Management System (PIMS). The 2019 edition has been withdrawn. | Official ISO page: ISO/IEC 27701:2025 |
| ISO/IEC 42001:2023 | International standard for an Artificial Intelligence Management System (AIMS). | Official ISO page: ISO/IEC 42001:2023 |
