

Supply Chain Risk Assessment Service (Panorays)
Visualize and centrally manage security measures across your entire supply chain to prepare for cybersecurity risks.
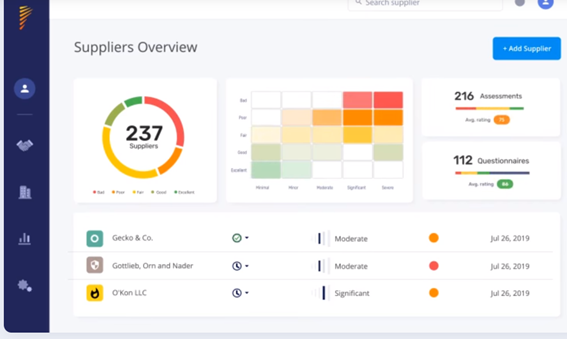
Using Panorays, a SaaS-based security risk assessment system provided by SOMPO Risk Management, we collect information about your suppliers in a shared system. This enables you to understand security measures across your entire supply chain, identify areas vulnerable to attack, and manage them centrally.
What Is a Supply Chain Security Risk Assessment?
Understand the security posture of your entire business supply chain and visualize its risks.
Supply chain attacks are on the rise. In these attacks, cybercriminals exploit supply chain partners that exchange highly confidential business information, such as domestic and overseas group companies and suppliers, as an entry point to target an organization.
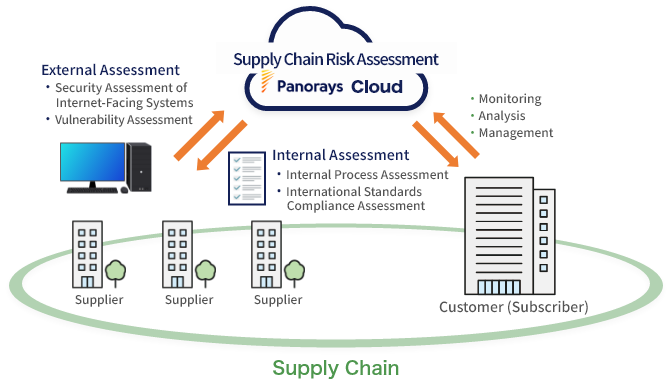
The Panorays cloud service collects information on the security measures of supply chain partners connected to your organization and consolidates it in a shared system, allowing you to visualize security issues and manage them centrally. It also includes assessment questions based on Infosec Advisory's security consulting expertise, enabling the effective identification of supply chain risks.
A free trial of the Panorays Supply Chain Risk Assessment is available.
If you are interested, please contact us below.
Visualize security risks across your organization by managing suppliers' external and internal security assessments throughout the supply chain using consistent criteria.
External Assessment
External assessments identify vulnerabilities without placing any load on or affecting the IT assets being assessed, eliminating the need to coordinate with individual system administrators. Rated security assessment results and their history can also be managed centrally. The remediation status of each IT asset can be reviewed in a single list, helping prevent missed actions.
The External Assessment (Vulnerability Assessment) feature automatically discovers and inventories internet-facing assets associated with your organization that may not yet be known and evaluates their vulnerabilities. Unlike vulnerability testing, it does not identify vulnerabilities by attempting attacks, so assessments can be performed without affecting the target assets.
Internal Assessment
The Internal Security Assessment feature provides ready-to-use questionnaire templates based on international information security standards and frameworks, including ISO 27001, GDPR, NIST, and IPA guidelines. Distribution, collection, and aggregation can all be managed centrally through a single cloud service. Security questionnaires can also be customized, allowing you to assess security risks according to your organization's specific requirements.
Supply Chain Risk Assessment Process
STEP1 Agree on the Scope and Define the Security Assessment
- Select suppliers and group companies and obtain their agreement to participate in the security assessment.
- Group the organizations in scope according to the confidentiality of their data and the importance of their business relationship.
- Prepare a questionnaire customized for your organization and determine the assessment period.
STEP2 Gather and Configure Company Information and Assessment Details
- Interview the companies being assessed to obtain information such as company names and domains.
- Register the collected information in Panorays, which automatically performs the external assessment.
- Provide the assessed companies with access to the system and instructions on how to use it.
STEP3 Conduct the Security Assessment
- Send security assessment requests to suppliers through the cloud service.
- Suppliers complete the security questionnaire through the cloud service.
- Assign quantitative risk ratings based on the external and internal assessments.
- Define corrective actions and develop an implementation plan for the identified issues.
STEP4 Monitor Security Regularly
- Conduct regular external and internal assessments, review the results, and develop corrective measures and implementation plans for identified issues.
A free trial of the Panorays Supply Chain Risk Assessment is available.
If you are interested, please contact us below.
